Cybersecurity Strategy
Strengthen security posture, resilience, incident readiness and enterprise cyber programs.
CYBERSECURITY • GRC • RESPONSIBLE AI
I connect cybersecurity, governance and responsible AI to help organizations turn complex risk into clear decisions.
INDUSTRY-LEADING CREDENTIALS
01 / THE WORK
Start with what matters to your organization. Explore the work behind each area of focus.
Strengthen security posture, resilience, incident readiness and enterprise cyber programs.
Build scalable governance, risk and compliance programs aligned to business priorities.
Establish responsible AI policies, controls, risk frameworks and operating models.
Build secure AI-powered tools and automations that solve real operational problems.
Translate cyber, GRC and AI complexity into clear priorities, decisions and organizational direction.
03 / CONVERSATIONS THAT MATTER
Keynotes, panels, podcasts and professional conversations that make cybersecurity, GRC and responsible AI clear and actionable.
Invite Natasha to speak →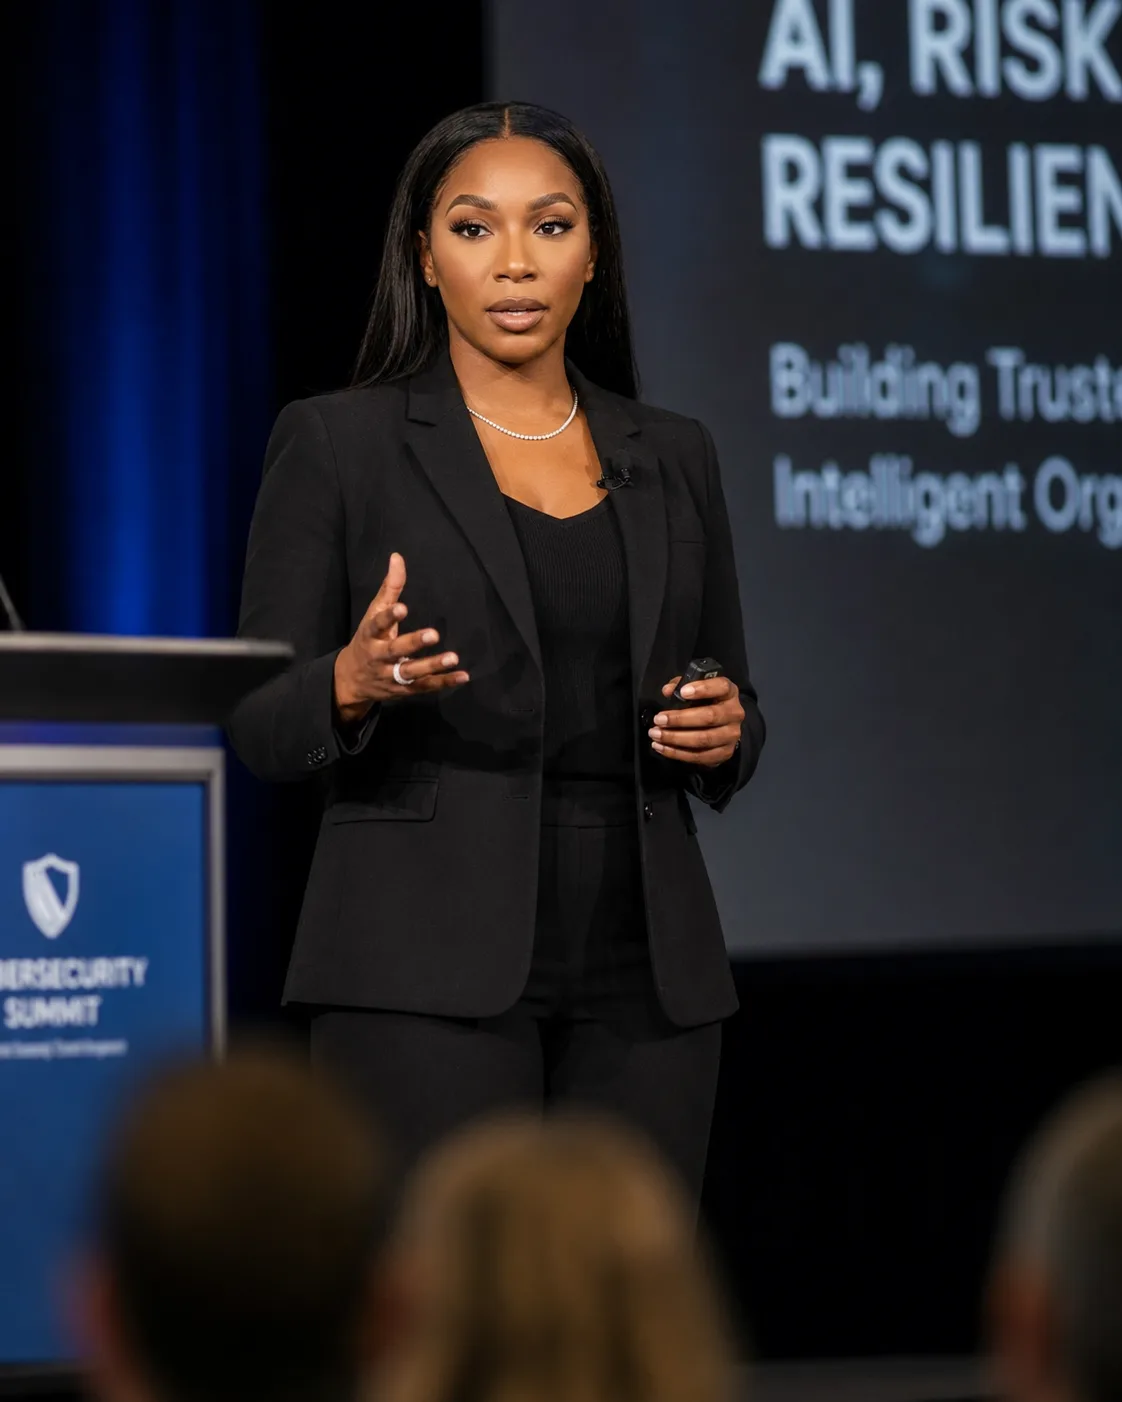
How organizations can move from AI experimentation to governance, accountability and sustainable adoption.
Building governance and risk programs that support decisions instead of becoming a paperwork exercise.
Connecting security strategy, operational resilience, culture and executive decision-making.
Lessons from applying security and governance principles to AI-powered tools and workflows.
02 / THE APPLICATION LAB
Explore small, working examples of governance in practice. Change the inputs and see how the next steps change.
INTERACTIVE DEMO
Try a fictional AI use case. These inputs determine which reviews to prioritize.
TECHNOLOGY PROCUREMENT • SAAS • THIRD-PARTY RISK
An AI-assisted workflow for reviewing technology, SaaS, cloud and AI-enabled vendor agreements through a cybersecurity, privacy, governance and operational-risk lens.
The workflow connects contract language to technology risk, required controls, governance decisions and recommended actions.
Vendor language permits customer information to be used for model training and product improvement.
OTHER APPLICATION CONCEPTS
AI GOVERNANCE
Intake AI use cases, identify risk indicators, classify review requirements and document governance decisions.
AI SECURITY
Evaluate AI-powered applications across architecture, identity, data flows, model usage, privacy, security controls and deployment readiness.
VENDOR GOVERNANCE
Examine vendors that use or provide AI and connect due-diligence findings to security, privacy, contractual and governance requirements.
Prototype portfolio. Functional labels describe the problems being explored and are not final product names.
04 / BUILD YOUR CAPABILITY
Coaching for professionals entering the field, expanding into governance and AI, or learning how to move from using AI tools to building and governing AI-powered applications.
Develop practical capability in how governance, risk and compliance operate inside real organizations — from assessing risk and designing controls to communicating results with leadership.
Learn how organizations move from experimenting with AI to governing it responsibly through repeatable risk, policy, security and oversight processes.
Move from an AI idea to a functioning application while learning how architecture, security, data, governance and deployment fit together.
READY TO GO DEEPER?
Share where you are now, what you are trying to accomplish and the skills you want to build.
05 / BEHIND THE WORK
I’m Natasha — a cybersecurity, GRC and AI leader focused on helping organizations make trust part of how they operate. My work brings together enterprise security strategy, risk management, responsible AI adoption and secure application development.
PERSPECTIVE & IMPACT
Build a practical GRC program stakeholders can actually use — with clearer accountability, stronger controls and better visibility into risk.
Create responsible AI guardrails that help organizations move faster without losing control of security, privacy or compliance.
Turn cyber and AI strategy into implementation — from governance and policy through secure applications, automation and measurable outcomes.
LET’S START A CONVERSATION
Explore a collaboration, invite a conversation, discuss cybersecurity or AI governance, or take the next step in your own practice.